Compliance Manager & Compliance Officer under the AMLR
The AMLR introduces significant changes to institutions' governance, with a new emphasis on the role of senior management. This article sets out the new requirements and their impact on obliged entities.

The (numerous) changes made by the AMLR include new governance requirements for obliged entities, set out chiefly in Chapter II AMLR (Art. 9-18 AMLR).
The basics
Art. 11 AMLR governs the structure and tasks of the compliance function. The compliance function to be established under Art. 11 AMLR consists of
- the Compliance Manager (Art. 11(1) UAbs. 1 AMLR) and
- the AML/CFT compliance officer ("Compliance Officer")
who together make up the compliance function.
This structure is nothing fundamentally new. The 5th AMLD already provided in Art. 46(4) that a responsible member of management had to be appointed for combating money laundering and terrorist financing, and Art. 8(4)(a) provided for the appointment of an AML/CFT compliance officer. What is new is the contour of the respective responsibilities and their effect on the liability of the Compliance Manager and the compliance officer (see below).
The Compliance Manager under the AMLR
Term and functional allocation
The Compliance Manager is a member of the management body in its management function, "responsible for ensuring compliance with this Regulation, Regulation (EU) 2023/1113 and any administrative acts issued by supervisors" (Art. 11(1) UAbs. 1 AMLR). The term is newly introduced by the AMLR.
The Compliance Manager must accordingly be a member of the management body (Art. 2(1) No. 5 AMLR) - and thus of senior management ("management body in its management function", Art. 2(1) No. 6 AMLR). The management level must be distinguished from the senior management level defined in Art. 2(1) No. 8. Allocating the Compliance Manager function at that lower level is not sufficient.
Responsibilities of the Compliance Manager
The Compliance Manager's duties include in particular the following:
Duty to ensure, Art. 11(1) UAbs. 2 AMLR
- The Compliance Manager must ensure that the obliged entity's internal policies, procedures and controls are consistent with the entity's risk profile and implemented (Art. 11(1) UAbs. 2 sentence 1 AMLR). The Compliance Manager therefore has to check, on the one hand, whether the rulebook developed matches the risk profile as it emerges from the business-wide risk assessment (adequacy of design). The second part of the exercise consists in checking the implementation of the rulebook, i.e. its effectiveness.
- The Compliance Manager must likewise ensure that adequate human and material resources are provided (Art. 11(1) UAbs. 2 sentence 2 AMLR). Responsibility that in principle rests with the obliged entity (Art. 11(3) AMLR) is thereby allocated to the Compliance Manager.
- Finally, the Compliance Manager is obliged to receive information about deficiencies. If the Compliance Manager obtains information about such deficiencies, they must take the necessary measures to remedy the deficiencies identified in a timely manner (Art. 11(6) sentence 4 AMLR).
Reporting duty, Art. 11(6) sentences 1-3 AMLR
The reporting duties set out in Art. 11(6) sentences 1-3 AMLR consist of three elements:
- Sentence 1 requires the Compliance Manager to report "regularly" on the implementation of the internal policies, procedures and controls in place. The AMLR does not further define what "regularly" means. The Compliance Manager therefore has to choose - and be able to justify - an appropriate frequency.
- As a rule annually, and where appropriate more frequently, the Compliance Manager reports on the implementation of the AML/CFT compliance officer's rulebook (Art. 11(6) sentence 2, 1st half-sentence AMLR). A shorter interval is likely to be called for in particular where material objections have previously been identified.
- At the same cadence, the Compliance Manager reports (formally) on the results of (internal and external) audits, for example by internal audit, the statutory auditor or the supervisor. Here too, considerably more frequent reporting is required where significant findings arise.
Duty to act, Art. 11(6) sentence 4 AMLR
The obligation under Art. 11(6) sentence 4 AMLR is likely one of the most severe for the responsible member of management, since they ultimately have to answer for an outcome - the taking of adequate measures. The EBA guidelines previously in force still provided here for a recommendation by the responsible member of the management body. The (indeterminate legal term) of "promptly" remedying deficiencies also opens the door wide to disputes with auditors and supervisors. Finally, the provision creates a dilemma for the Compliance Manager: they must ensure the relevant outcome (the remedying of the shortcomings) but do not have sole decision-making authority over the measures needed to remedy them. To relieve the Compliance Manager, a clarification in the rules of procedure of senior management is advisable here.
Approval of policies, procedures and controls, Art. 9(2) UAbs. 3
The procedure for approving the written rulebook, as it is to be developed by the AML/CFT compliance officer, is likewise staggered:
- Internal policies must be approved by the management body in its management function;
- Internal procedures and controls are approved at least at the level of the Compliance Manager. The Compliance Manager can therefore decide alone on the sign-off of such procedures and controls - but can also require sign-off by senior management as a whole.
Relationship to senior management as a whole
Allocating responsibilities to the Compliance Manager does not relieve senior management as a whole of its overall responsibility. Recital 38, sentence 2 expressly clarifies that appointing a responsible member as Compliance Manager does not change the fact that overall responsibility "ultimately rests with the entity's management body" . In collegially organised bodies, the Compliance Manager's role is to "support and advise the body and to prepare its decisions".
Allocating a specific portfolio in this way changes nothing about the continuing supervisory duty of the other members of senior management - meaning that regular reports at senior management meetings on the risk situation and the adequacy of the controls implemented (including their effectiveness) should be a mandatory agenda item.
Correspondingly, Art. 11(5) AMLR provides that the AML/CFT compliance officer reports to the (entire) management and supervisory function, and specifically not exclusively to the Compliance Manager.
The approval cascade shows the Compliance Manager as an intermediate layer, not a substitute for the body:
| Subject matter | Who approves |
|---|---|
| Internal policies | Management body in its management function (Art. 9(2) UAbs. 3 sentence 2) |
| Internal procedures and controls | at least the Compliance Manager (Art. 9(2) UAbs. 3 sentence 3) |
| Business-wide risk assessment | Management body in its management function — not the Compliance Manager (Art. 10(2) UAbs. 2) |
Compliance Officer
Duties of the Compliance Officer
Unlike the Compliance Manager, the AMLR does not define the term Compliance Officer, i.e. AML/CFT compliance officer. Art. 11(2) UAbs. 1 AMLR provides the central definition:
Obliged entities must have an AML/CFT compliance officer, to be appointed by the management body in its management function, who has a sufficiently senior position in the hierarchy and is responsible for the policies, procedures and controls in the day-to-day implementation of the requirements for combating money laundering and terrorist financing applicable to the obliged entity, including with regard to the implementation of targeted financial sanctions, and who serves as the point of contact for the competent authorities. The AML/CFT compliance officer is also responsible for reporting suspicious transactions to the central Financial Intelligence Unit under Article 69(6).
The AML/CFT compliance officer is thus responsible for:
- ongoing ("day-to-day") implementation of the requirements to combat money laundering and terrorist financing,
- compliance with targeted restrictive measures,
- acting as point of contact for authorities, and
- filing suspicious transaction reports.
Changes compared to the current legal position
From the exception to the rule
For the non-financial sector, the key change is the abolition of the exceptions and relief currently available. Whereas under Section 7 GwG an AML/CFT compliance officer only had to be appointed in the cases specified in Section 7(1) sentence 1 GwG, and the competent supervisory authorities could otherwise only order the appointment of an AML/CFT compliance officer in all other cases (Section 7(3) GwG), Art. 11(2) AMLR provides for the appointment of an AML/CFT compliance officer for all obliged entities .
Protecting independence
The independence of the AML/CFT compliance officer is significantly strengthened under the AMLR (see Art. 11(2) UAbs. 4 AMLR):
- On the one hand, dismissal requires a prior notification of the entire senior management;
- before dismissal, the (planned) dismissal must be notified to the supervisor, including information on whether the dismissal is connected with the performance of the officer's duties;
- the AML/CFT compliance officer is given an independent right to information vis-à-vis the supervisor.
The AML/CFT compliance officer's decision-making authority is also significantly strengthened (Art. 11(4) AMLR):
- Art. 11(4) AMLR protects the AML/CFT compliance officer against retaliation, discrimination and any other unfair treatment;
- a particular protection lies in the fact that decisions of the AML/CFT compliance officer must "not be impaired or improperly influenced by the obliged entity's commercial interests" .
The final requirement carries real force: obliged entities must ensure that commercial interests do not jeopardise the performance of these duties. Senior management therefore bears the burden of demonstrating that decisions taken against the advice of the AML/CFT compliance officer were not taken for commercial reasons.
Under Art. 11(5) AMLR, the AML/CFT compliance officer is entitled to report directly to the management body in its supervisory function, including the right to raise concerns and warnings. The exceptional case previously provided for in Section 7(5) sentence 5 GwG thus becomes the rule.
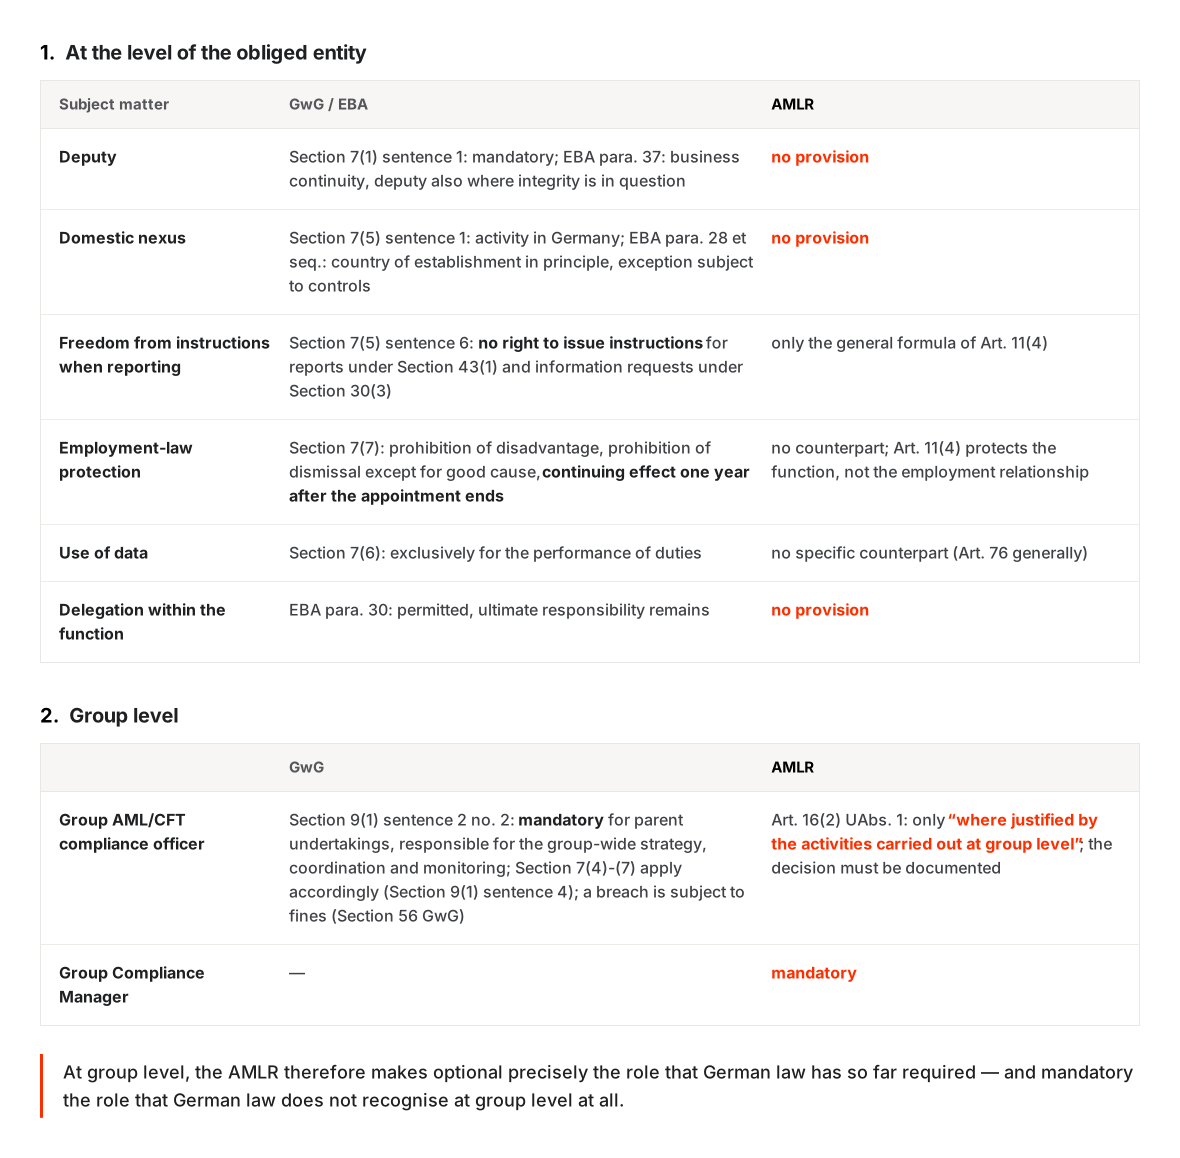
Further changes
Conclusion
The AMLR's requirements place considerably greater emphasis than before on the responsibility of the Compliance Manager as the responsible member of the management body. This relieves the AML/CFT compliance officer to a certain extent. Given the case law on the AML/CFT compliance officer's personal liability (see, by way of example, the judgment of the Frankfurt Higher Regional Court of 10 April 2018 - 2 Ss-Owi 1059/17, and by contrast the CJEU judgment of 29 January 2026 - Case C-291/24, see also the article by Preni Giragosian) this is a welcome development.
For companies, this means adjustments to their governance, in particular at the level of senior management.